
If you’re a property manager, you sit on a pile of personal data. You might not call it that, but that’s what it is. Tenant records are high-value because they’re useful for fraud, and they’re easy to weaponize for phishing.
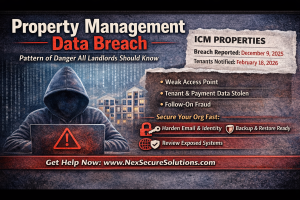
ICM Properties, Inc. reported an external system breach (hacking) with incident date December 9, 2025 and consumer notification dated February 18, 2026.
What matters for other property management firms is not the name. It’s the pattern.
Attackers don’t need you to be famous. They need you to be reachable. A portal, a VPN, an exposed admin interface, or a compromised email account is enough.
Here’s how it usually plays out in small orgs:
-
They get access through a weak identity path or exposed system.
-
They move quietly, looking for tenant data, payment workflows, and vendor contacts.
-
They steal records and then use them to launch follow-on fraud.
If you want to reduce your risk fast, focus on three things:
-
Email and identity hardening. MFA enforced, legacy auth off, admin accounts separated from daily accounts.
-
Backup readiness. Prove restore works, not just that backups exist.
-
Exposure review. What’s internet-facing, who has admin, and what SaaS holds tenant data.
Week 1 with NexSecure looks like this:
-
Rapid assessment focused on identity, exposure, and tenant-data systems.
-
KEV-first patch prioritization with verification, including reboot and version proof when required.
-
A short incident-ready runbook so you’re not making decisions for the first time during a breach.
Read more on my blog: https://nexsecuresolutions.com/blog/
If you want help implementing this, here’s how we support SMBs: https://nexsecuresolutions.com/cybersecurity-services/
NexSecure Solutions helps small organizations reduce cyber risk through practical reviews, clear priorities, and senior cybersecurity guidance. Schedule a free discovery call.